// case study — 2024
simpletaste.pt
I worked on cybersecurity and performance optimization for SimpleTaste.pt, improving application code, PHP and MySQL services. The project included CVE vulnerability remediation and integration with Dotec's proprietary security monitoring and sentinel systems.
 // client — Simple Taste →

// on this page (13)
Project: SimpleTaste.pt — eCommerce cybersecurity, performance optimization and infrastructure monitoring
My Role: Security analysis, vulnerability remediation, code updates, service optimization, technical administration and monitoring system integration.
Tech Stack: PrestaShop, PHP, MySQL, web infrastructure and Dotec's proprietary monitoring and sentinel systems.
An online store can have an attractive design, an extensive product catalogue and a well-organized shopping experience. But there is another equally important part that customers rarely see: the code processing every request, the database storing information and the services keeping everything running.
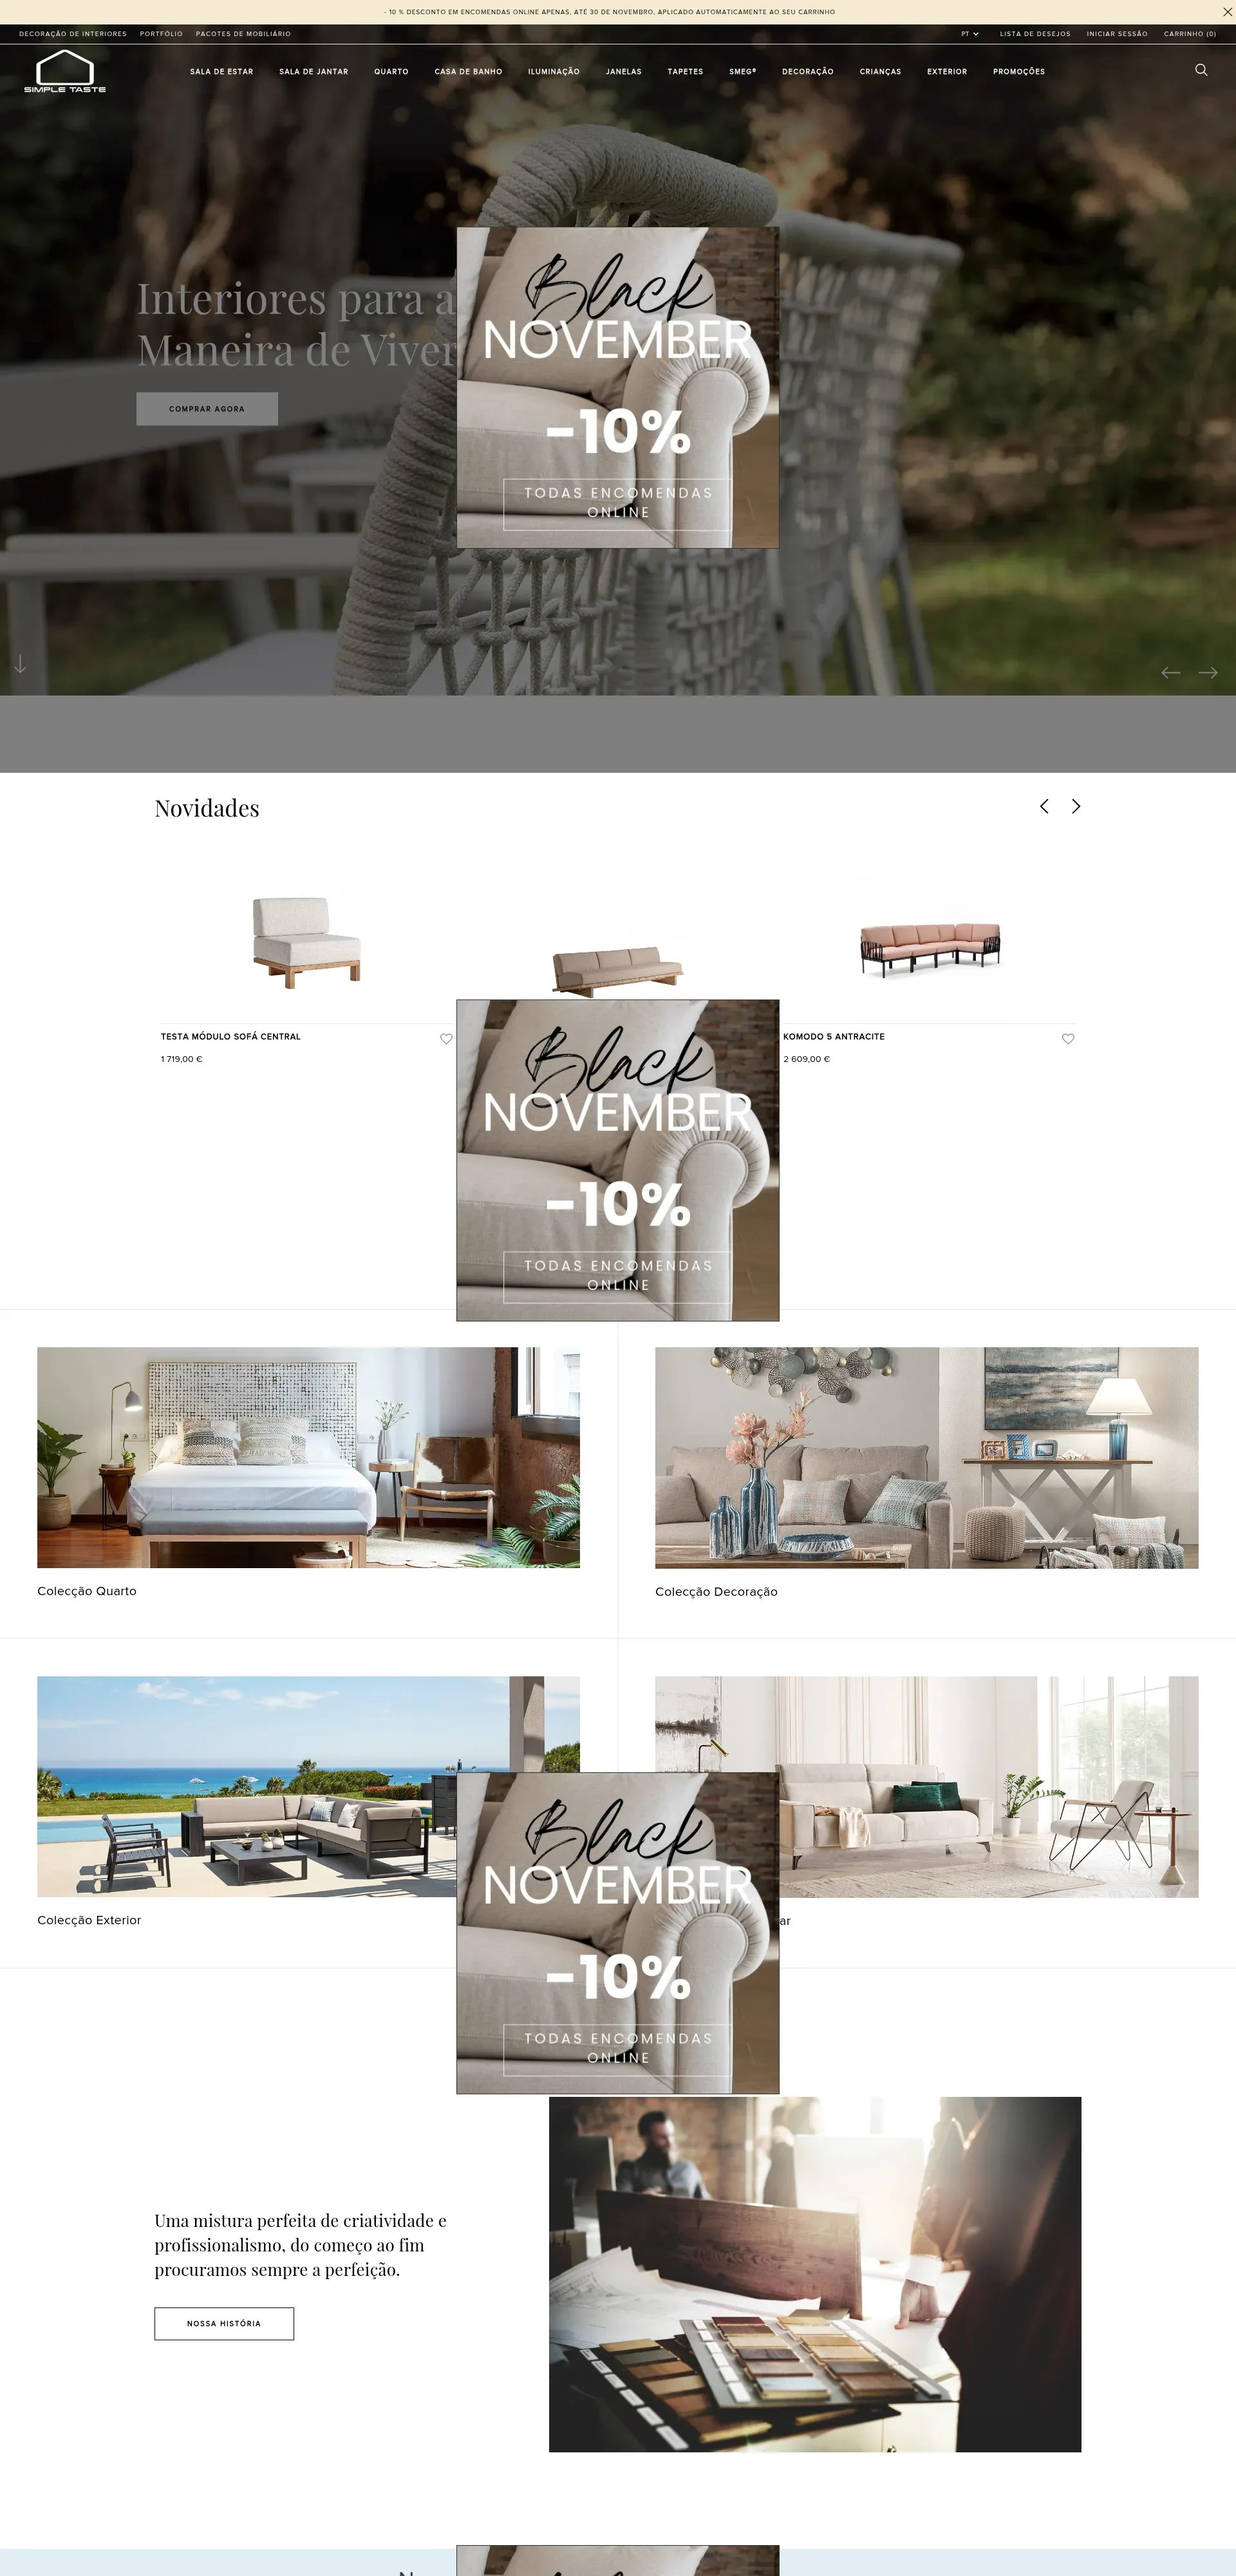
That was exactly where my work on simpletaste.pt was focused. The website belongs to Simple Taste Interiors, a Portuguese company specializing in furniture, home décor and interior design.
Unlike other projects where I've been involved from the initial development stages, my responsibilities here were quite specific: improving the security and performance of an existing eCommerce platform.
The project involved analyzing and updating code, addressing known security vulnerabilities, optimizing the application and its PHP and MySQL services, and integrating the infrastructure with proprietary monitoring systems developed and maintained by Dotec.
My goal was to reduce security risks, improve service performance and establish better technical oversight of the platform's operation.
The Challenge: Improving an Existing Store Without Disrupting Its Operations
Working on a production environment is quite different from building a website from scratch.
There is already an application running, an established database structure and a collection of features used every day by customers and the team managing the store.
A seemingly minor change can have unexpected consequences. Updating code may affect module compatibility. Changing PHP settings can alter how certain features behave. And modifying a database configuration may improve one operation while negatively affecting another.
For SimpleTaste.pt, the challenge was to examine the different technical layers and identify where security and performance improvements could be made.
This wasn't a project about redesigning the store or developing new commercial features. My work focused on the components supporting the existing application and keeping its services operational.
I wanted a more secure platform, better response times and an infrastructure that could be monitored and managed more effectively.
Cybersecurity — Analyzing Code and Reducing Vulnerabilities
One of my main responsibilities was application cybersecurity.
eCommerce platforms depend on multiple software components. Beyond the core system, they often include modules, libraries, external services and custom code developed for particular business requirements.
This combination makes an online store flexible and functional, but it also introduces security considerations.
A vulnerability in one component may expose information, compromise certain operations or allow behavior that should never be possible.
Part of my work therefore involved analyzing the code and identifying components that required security corrections or updates.
These changes had to be considered alongside the application's existing behavior. Fixing a security issue should not mean breaking a feature the business depends on.
Security improvements needed to remain compatible with the platform's dependencies and operational requirements.
The objective was to reduce exposure to known vulnerabilities without compromising the store's normal operation.
CVE Vulnerability Remediation — Updating Vulnerable Code
An important part of the project involved updating code to address security vulnerabilities documented through CVE — Common Vulnerabilities and Exposures.
CVEs are publicly assigned identifiers used to document known software security vulnerabilities. They help developers and security professionals identify affected components, understand technical risks and determine which versions may require remediation.
This information is particularly relevant in eCommerce, where different modules and software libraries may not always receive updates at the same time.
My work involved identifying vulnerable code and applying the necessary security corrections while considering their potential impact on the existing platform.
Not every security update can be handled by simply replacing a few files. Dependencies need to be understood, and changes must preserve the expected behavior of the application.
That was the approach I followed when working on security updates for SimpleTaste.pt.
The focus was on addressing known issues, reducing the attack surface and maintaining compatibility between updated components and the rest of the system.
For me, vulnerability management doesn't end when a patch has been applied. Newly disclosed issues and changes to software dependencies also need ongoing attention.
PrestaShop — Application-Level Security and Performance
SimpleTaste.pt uses PrestaShop, an eCommerce platform built with PHP and supported by a relational database.
Running a PrestaShop store involves many operations happening continuously: loading products, retrieving categories, calculating prices, managing sessions and communicating with the database.
As a store grows and incorporates additional modules or code modifications, understanding the performance impact of these operations becomes increasingly important.
My intervention included optimizing the store's application code, focusing on improving execution efficiency and reducing unnecessary processing.
This required understanding the existing structure and how different application components interacted.
Security updates also needed to remain compatible with the platform's operational requirements, avoiding changes that could introduce unexpected problems.
The challenge was to improve the application's technical behavior without changing the shopping experience customers already expected.
In eCommerce, performance and security should not be treated as unrelated concerns. Both contribute to service stability and reliability.
Performance Optimization — Improving Application Efficiency
An online store performs far more operations than those visible in a browser.
When someone opens a product category, the application needs to retrieve information, process results, prepare product data and generate the page returned to the visitor.
If some of that processing is unnecessarily expensive, response times can increase even when the server has sufficient resources available.
That is why code optimization was one of the areas I worked on at SimpleTaste.pt.
Performance analysis involved examining the efficiency of application operations and the relationship between code execution, database processing and the PHP environment.
This type of work requires understanding what happens between an incoming request and the response delivered to the browser.
It is also important to recognize that slow response times do not always have the same cause.
A page might be slow because of expensive database queries, excessive application processing or limitations in the resources available to a particular service.
Rather than treating performance as a purely visual matter, I approached it as a characteristic of the entire system.
The goal was to improve application efficiency and the responsiveness of the services supporting it.
MySQL — Database Performance Optimization
The MySQL database is one of the most important components of an online store.
It stores information about products, categories, customers, orders, settings and many other application features.
During everyday browsing, PrestaShop continuously executes database queries. Some are relatively straightforward, while others involve several tables, filtering operations and more demanding processing.
When database performance fails to keep up with application requirements, slowdowns can affect several parts of the store.
My work included optimizing MySQL services, focusing on processing efficiency and the use of available resources.
Database performance needs to be analyzed alongside the application using it. Increasing server resources does not always solve a problem caused by inefficient application behavior.
That is why I prefer working on both sides of the equation: the application code generating queries and the database service executing them.
Improving the relationship between these components makes it possible to address performance problems at their source rather than simply compensating for them with additional computing resources.
PHP — Optimizing the Execution Environment
Another important part of the project involved PHP service optimization.
PHP executes much of the application's business logic. Individual requests may involve loading code, processing data, applying commercial rules and communicating with the database.
Performance depends not only on code quality, but also on the environment where that code runs.
PHP configurations influence memory usage, execution behavior and how the server handles incoming requests.
I worked on this layer to better align the execution environment with the requirements of the online store.
Optimization also required attention to compatibility between PHP and the platform's existing components.
Overly restrictive settings can cause failures, while inappropriate configurations may increase resource consumption without providing meaningful improvements.
The challenge was finding the right balance between performance, stability and application requirements.
Application, PHP and MySQL — Three Layers Working Together
One of the defining technical aspects of this project was the need to approach performance at different levels.
The store's code, PHP and MySQL do not operate independently. A request originating in the application may involve PHP processing, multiple database queries and additional work before a response reaches the browser.
If one of these layers experiences difficulties, the behavior of the entire system can be affected.
For example, an inefficient database query may increase PHP execution time. Longer-running requests can then occupy resources for extended periods, potentially reducing the capacity available to other visitors.
This chain reaction is one of the reasons application and server optimization require an understanding of the entire infrastructure.
At SimpleTaste.pt, my work covered these interconnected components: application code, PHP services and MySQL database processing.
The objective was not to improve one isolated metric, but to contribute to greater overall efficiency.
Dotec Sentinel Systems — Infrastructure Monitoring
Alongside the security and performance improvements, I integrated SimpleTaste.pt with Dotec's proprietary sentinel and monitoring systems.
These systems form part of the technical solutions Dotec uses to monitor infrastructure and services under its management.
The integration brought the project into a monitoring environment, adding a technical oversight component to the work carried out on the application.
Infrastructure can experience unusual behavior even when a website appears accessible. Performance issues, service failures or unexpected changes may not be immediately obvious to someone browsing the store.
That is why I consider it important to monitor the systems beyond what visitors can see.
Monitoring makes it possible to observe service behavior and identify situations that may require further technical investigation.
By integrating SimpleTaste.pt into Dotec's monitoring environment, I complemented the security corrections and performance improvements with additional technical oversight.
The idea was not simply to intervene when a problem appeared, but to establish better conditions for understanding how services behave and following their evolution.
Cybersecurity and Monitoring — A Preventive Approach
Fixing known vulnerabilities is an important part of security, but it does not mean an application is no longer exposed to risks.
New vulnerabilities may be discovered, software components can become outdated and environmental changes may introduce problems that did not previously exist.
For that reason, cybersecurity needs to be treated as an ongoing process.
At SimpleTaste.pt, my intervention combined two complementary areas: addressing identified vulnerabilities and integrating services with a monitoring system.
This approach connects application maintenance with the observation of infrastructure behavior.
Monitoring is not a substitute for a security assessment, just as installing software updates does not eliminate the need for code analysis. They are different measures with different purposes.
When used together, however, they contribute to a more consistent approach to the technical management of an online platform.
Stability and Service Continuity in eCommerce
In an online store, platform availability is directly connected to commercial activity.
If customers cannot browse products, access their shopping baskets or complete an order, a technical issue quickly becomes a business problem.
SimpleTaste.pt offers a furniture and home décor catalogue covering different categories and collections. Accessing this information depends on the application and its supporting services functioning correctly.
Security and performance improvements therefore had a practical purpose: contributing to the stability and reliability of the online store.
Improving processing efficiency, reducing compatibility problems and monitoring services are not activities that customers will see on a product page.
Nevertheless, they influence the quality of the service available to customers and the conditions under which the team can manage the platform.
This is an area of development and system administration that I consider particularly valuable, because the benefits should be reflected in everyday use even when the technical work itself remains invisible.
The Result — Greater Focus on Security, Performance and Monitoring
My work on SimpleTaste.pt focused on three technical areas: Cybersecurity, Performance Optimization and System Administration.
The project involved reviewing and updating code to remediate CVE vulnerabilities, optimizing the PrestaShop application, improving PHP and MySQL services, and integrating the infrastructure with Dotec's proprietary sentinel systems.
These interventions were designed to reduce security risks, improve service efficiency and establish a foundation for ongoing technical monitoring.
I wasn't responsible for designing the store or developing its commercial features. My role was to work on the components supporting the application, improving what happens behind the interface.
This kind of work requires knowledge of software development, databases, system administration and cybersecurity, as well as the ability to understand how these areas interact.
More than simply changing configurations or updating files, the challenge was to understand the platform's behavior and identify the areas where technical improvements could make a difference.
Not All Important Work Is Visible
The SimpleTaste.pt project represents a part of my professional work that often goes unnoticed by people using a website.
Not every project requires building a new store, developing a new design or adding features. Sometimes the most valuable contribution is understanding what already exists and finding ways to make it work better.
In this case, my responsibilities involved code security, service optimization and integrating the infrastructure with Dotec's monitoring technology.
These technical areas have a direct impact on how an application operates, even when they produce no obvious visual changes.
This is also where my experience in Full Stack Development, System Administration and Cybersecurity comes together. I can investigate problems from the application through to the services executing it, without treating each component as an entirely separate system.
Because in an online store, what customers see matters. But what happens behind the screen is what keeps everything running.
// project details
- client
- Simple Taste
- year
- 2024
- platform
- PrestaShop
- role
- Fullstack Developer
- Module Development
- Security Analyst
- Performance Optimization
- stack (17)
-
- PHP
- PHP-FPM
- PrestaShop
- Smarty
- Symfony
- MySQL
- HTML
- CSS
- JavaScript
- jQuery
- Cloudflare WAF
- ModSecurity
- Fail2ban
- Let's Encrypt
- Redis
- OPcache
- Cloudflare CDN